How to manage SSH access in Kiravo
Open your website in the hosting control panel and choose Advanced → Developer tools. SSH key manager manages public keys for SSH/SFTP. SSH password authentication shows the password-login controls.
SSH grants command-line access to the website’s environment. An uploaded key applies to the whole website, including its domains. It is separate from a directory-limited FTP account.
Prepare a key pair
Section titled “Prepare a key pair”Use a terminal with OpenSSH installed. To create a separate key for this website on macOS or Linux:
ssh-keygen -t ed25519 \
  -f ~/.ssh/kiravo_ed25519 \
  -C "kiravo-laptop"
Choose a different filename if that file already exists. Do not overwrite a key used for another connection. Set a passphrase to protect the private key.
The command creates a private key at ~/.ssh/kiravo_ed25519 and a public key at ~/.ssh/kiravo_ed25519.pub. Upload only the .pub file. Keep the private key on your computer and do not paste it into the panel, a support ticket, or chat. See the OpenSSH key-generation manual for other options.
Upload the public key to Kiravo
Section titled “Upload the public key to Kiravo”- Select SSH key manager, then click Add.
- Enter a Name that identifies the person or device, such as “Work laptop”.
- Paste the public key into Public key, or use Upload file to select its
.pubfile. - Review the website and key, then click Upload. Use Cancel to leave without granting access.
- Check that the intended key appears in the list before testing the connection.
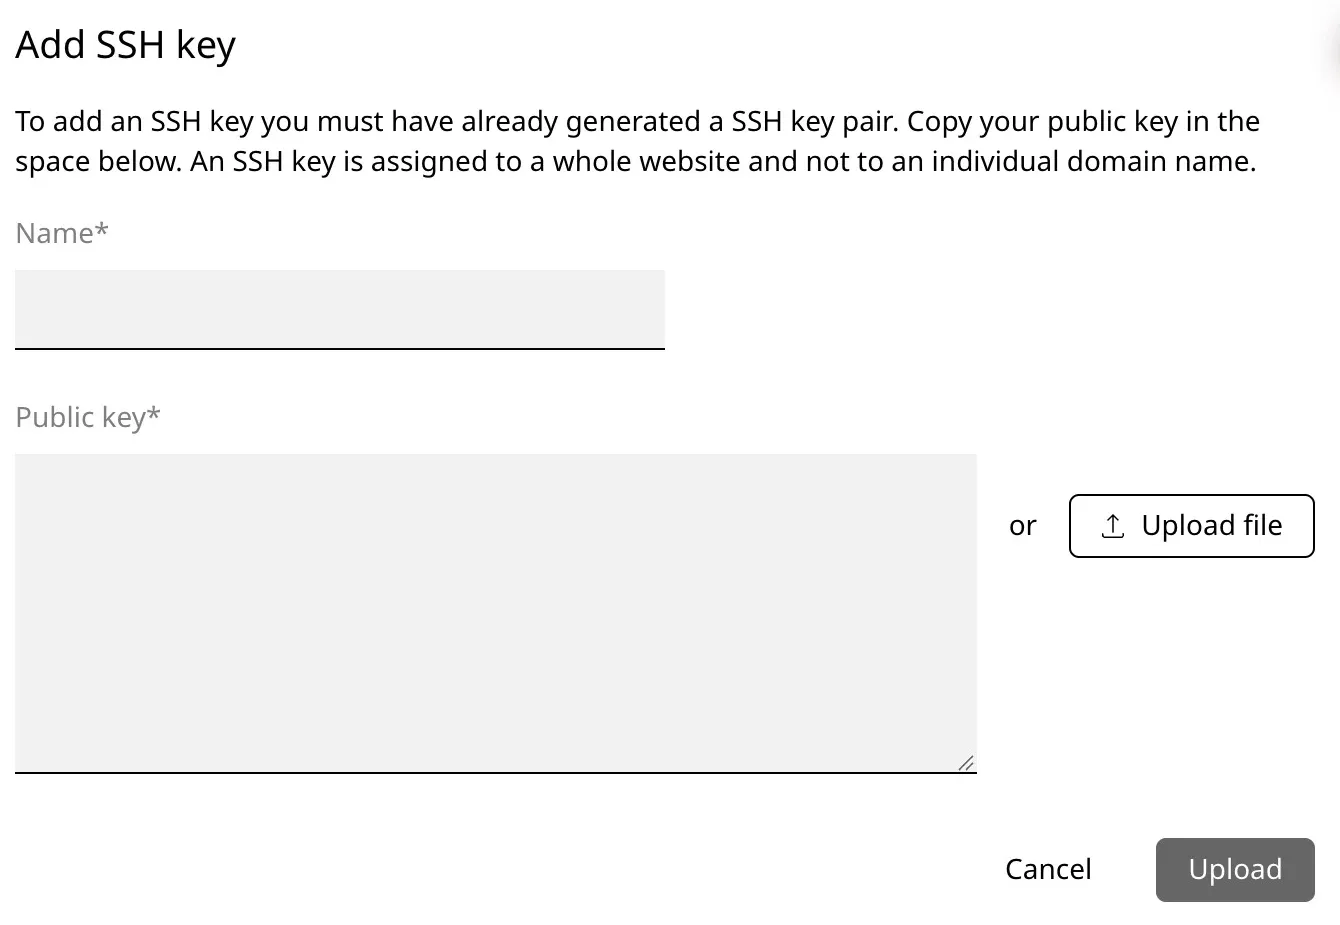
Give each collaborator or device a separate key so you can identify and remove access individually. Do not upload a private key or a file beginning with a private-key header.
Connect with the key
Section titled “Connect with the key”SSH key manager shows the website’s login command. Copy its username, server, and port rather than guessing from the domain or your Kiravo email address.
Use that command with the -i option when your private key has a custom filename. This example uses placeholders:
ssh -i ~/.ssh/kiravo_ed25519 \
  -p PORT USERNAME@SERVER
Replace PORT, USERNAME, and SERVER with the values from the panel. The -i path identifies the private key on your computer. OpenSSH may ask for its passphrase. See the OpenSSH client manual for these options.
On the first connection, verify the server’s host-key fingerprint using a trusted value from support before accepting it. Stop and verify an unexpected host-key change instead of deleting the known-host entry to suppress the warning.
After connecting, use a read-only command such as pwd to confirm the environment before changing files. Finish with exit.
SSH password authentication
Section titled “SSH password authentication”Select SSH password authentication to find Login command and the masked Password field with Reset. This is the website’s SSH password, separate from your client-area, WordPress, database, and FTP passwords.
Use Reset only when you intend to change that credential. Follow the panel’s prompts, store the resulting password securely, and update saved connections or tools that use it. Do not reset the password merely to look up the username or server; both are in the login command.
For password login, use the displayed command and enter the SSH password when the terminal prompts. Do not append the password to the command line.
If the connection fails
Section titled “If the connection fails”- Permission denied: check the panel’s username, selected private key, and whether the matching public key is listed for this website.
- Timeout or refused connection: compare the host and port with the login command and check whether the service permits SSH access.
- Private-key file error: check that the local path points to the private key and that other users cannot read it.
- Wrong files after login: confirm the selected website and current directory before running commands.
Contact support with the time and error text if access still fails. Do not send private keys, passwords, or unredacted authentication logs.
Remove access
Section titled “Remove access”Use the delete control beside the public key you intend to remove and check its name before confirming. Test any replacement key before removing your only working method of access.
Removing a public key does not revoke separate password, FTP, or panel access. Review those credentials when a collaborator leaves. If a private key is exposed, replace it and remove its corresponding public key wherever that key was authorized.